TL;DR

Get the little things that make your day delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
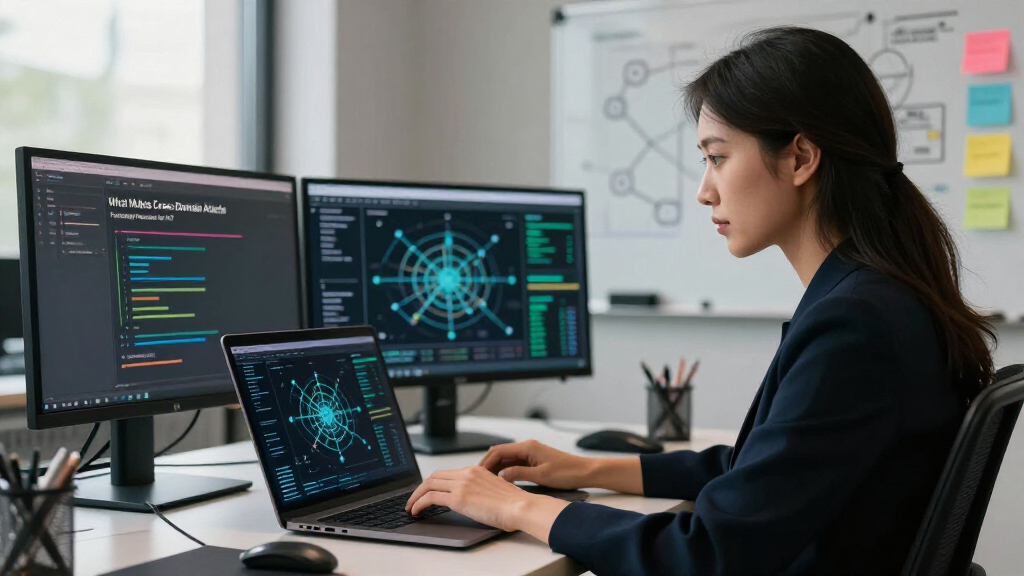
Cross-domain attacks leverage multiple operational domains to create cascading effects and ambiguity, making AI systems vulnerable in ways that are hard to detect and respond to promptly. This raises significant concerns for national security and AI integrity.
Recent security analyses emphasize that cross-domain attacks pose a significant threat to AI systems due to their ability to generate cascading effects, ambiguity, and political paralysis. Unlike traditional single-domain threats, these multi-faceted operations target the interconnected infrastructure and decision-making processes, making responses difficult and delayed. This development is critical as AI becomes embedded in vital systems, increasing the potential impact of such attacks.
Experts from cybersecurity and defense fields warn that multi-domain operations are no longer confined to physical or cyber realms alone but involve complex interactions across space, electromagnetic spectrum, and information domains. These attacks aim not just to damage infrastructure but to produce strategic effects by exploiting the interconnected dependencies of modern systems.
One core mechanism is the cascade effect: a limited action in one domain can propagate through interconnected civilian and military infrastructure, amplifying damage beyond initial targets. For example, a cyberattack on space-based signals could disrupt finance, logistics, and communications, triggering widespread systemic failure.
Another critical aspect is threshold and attribution ambiguity. Attackers calibrate operations to remain below the level that would trigger collective or legal responses, intentionally blurring attribution to avoid retaliation. This strategic ambiguity targets the decision-making threshold—the point at which authorities recognize an attack and respond—thus paralyzing collective action.
Finally, the cognitive and political impact focuses on eroding alliance cohesion and trust. By creating confusion and doubt about the nature and origin of attacks, adversaries aim to fracture consensus, weaken collective response mechanisms, and undermine systemic resilience.
Implications for National Security and AI Integrity
This evolving threat landscape underscores the importance of developing advanced sensing and fusion capabilities to detect multi-domain, coordinated attacks against AI systems. The ability to recognize complex, ambiguous patterns early is vital to prevent cascading failures and political paralysis. Failure to adapt could result in delayed responses, increased systemic vulnerability, and diminished trust in AI-driven infrastructure, with potentially catastrophic consequences for national security and economic stability.
As an affiliate, we earn on qualifying purchases.
The Rise of Multi-Domain Warfare and AI Vulnerabilities
Over recent years, military and security strategies have shifted toward multi-domain operations, integrating land, air, maritime, cyber, space, and information spheres. This shift reflects an understanding that modern conflicts are less about isolated strikes and more about orchestrated, layered effects across interconnected systems. AI systems, increasingly embedded in critical infrastructure, are now prime targets within this framework.
Historically, threats focused on physical destruction or cyber disruption; however, recent analyses, including those discussed by Thorsten Meyer, highlight that the true danger lies in the cascade effects and ambiguity that these multi-domain attacks can produce. The strategic advantage for adversaries is not just damage but the paralysis of response mechanisms and the erosion of alliance cohesion.
“The impact of a cross-domain attack is not measured primarily in territory or casualties but in the thresholds, cohesion, and systemic resilience.”
— Thorsten Meyer
Unclear Aspects of Detection and Response Capabilities
While experts agree on the threat posed by cross-domain attacks, it remains unclear how effective current detection systems are at recognizing coordinated, multi-domain operations in real time. The ability to fuse signals across diverse domains quickly enough to respond before thresholds are crossed is still under development. Additionally, the precise impact of these attacks on AI decision-making processes and infrastructure resilience is not fully understood, with ongoing research needed to quantify risks and develop countermeasures.
Advancing Detection, Attribution, and Resilience Strategies
Future efforts will focus on enhancing multi-domain sensing technologies, improving fusion algorithms, and establishing rapid attribution protocols to identify coordinated attacks swiftly. Policymakers and defense agencies are expected to prioritize investments in AI-driven detection systems capable of recognizing subtle, ambiguous patterns indicative of multi-domain operations. Strengthening resilience of critical infrastructure and developing international norms against such tactics will also be key components of ongoing strategies.
Key Questions
Why are cross-domain attacks more dangerous than single-domain attacks?
Because they can produce cascading effects across interconnected systems, making damage more widespread and difficult to contain. They also exploit ambiguity to delay or prevent response, and target decision thresholds and alliance cohesion.
How do attackers maintain ambiguity in their operations?
By calibrating actions to stay below response thresholds and by blurring attribution through sophisticated, multi-layered tactics that make it difficult to identify the true source or intent.
What makes detection of these attacks particularly challenging?
Signals are dispersed across different domains with little natural overlap, requiring advanced fusion and analysis capabilities to recognize coordinated patterns in real time.
What can be done to improve defenses against cross-domain attacks?
Investing in AI-enhanced sensing and fusion systems, establishing rapid attribution protocols, and strengthening systemic resilience are critical steps to counter these threats effectively.
Why is this issue relevant now?
As AI systems become integral to national security and critical infrastructure, adversaries are increasingly employing multi-domain tactics to exploit vulnerabilities, making this a pressing concern for policymakers and technologists.
Source: ThorstenMeyerAI.com
NFL season / tailgating Picks
team gear
As an affiliate, we earn on qualifying purchases.